When you hear about a cyber attack, you probably think of stolen data, hacked email accounts or ransomware bringing office computers to a standstill.
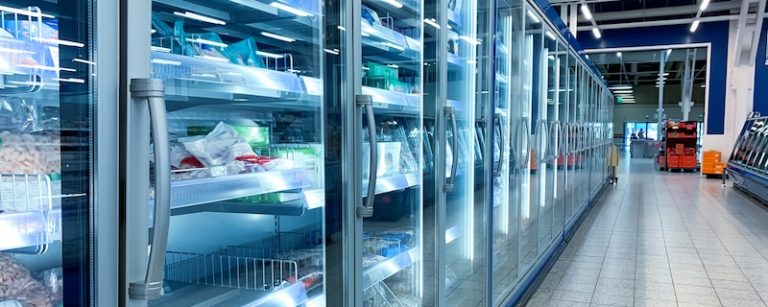
Supermarket freezers are less likely to spring to mind. Yet that’s exactly what has been making the headlines following cyber attacks on refrigeration systems across Europe.
Hackers have reportedly gained access to connected refrigeration controls, changing temperatures and leaving supermarkets with spoiled food and disrupted operations. The incidents have also affected a small number of businesses in the UK food supply chain, prompting warnings from the National Cyber Security Centre (NCSC).
It’s an unusual story, but one we’re likely to hear more about. It also raises a security concern that’s relevant to many businesses.
Think about the technology that keeps your own premises running. Heating and ventilation systems, security cameras, electronic access controls and other connected equipment all play a part in day-to-day operations. Some of these systems can be monitored and managed remotely, often by external suppliers. That’s useful, particularly for businesses operating across multiple locations, but it also means thinking carefully about how those connections are secured. And it’s an area that can easily be overlooked.
Quick Summary
Recent cyber attacks on supermarket refrigeration systems have highlighted the risks associated with internet-connected equipment. Businesses increasingly rely on connected technology, from heating and building controls to security cameras and access systems. If these devices aren’t properly secured, they could provide opportunities for attackers or cause disruption to everyday operations. Knowing what’s connected to your network, controlling remote access, keeping equipment updated and understanding who’s responsible for its security are important steps in reducing the risk.
Connected equipment brings its own security risks
Network-connected technology has become a normal part of running a business, often without us giving it much thought.
Take heating and ventilation systems, for example. An engineer may be able to check equipment performance, investigate a fault or adjust settings remotely without visiting the premises.
Similar technology is used in care settings, where connected building controls, access systems and monitoring equipment can support everyday operations. Offices and commercial buildings also rely on networked security cameras, automated heating and other connected systems.
For M&E contractors and building services businesses, remote connectivity can be particularly useful when managing equipment across different sites.
You may have heard these systems described as the Internet of Things (IoT) or Operational Technology (OT). IoT generally refers to physical devices that exchange information over a network. OT describes technology used to monitor or control physical equipment and processes. The terminology is useful, but from a business perspective, the important question is how these systems connect to your network and who can access them.
A security camera and a refrigeration control system serve very different purposes, so the risks associated with them won’t be identical. However, both could create problems if someone gained unauthorised access. Where connected equipment supports essential services, the consequences can be particularly serious. An interruption to heating, building access or other important systems could affect staff, customers and the people who depend on those services.
Why does connected equipment become vulnerable?
Reports about the European refrigeration attacks have raised concerns about ageing technology, insecure internet connections and equipment using default passwords. These are familiar cyber security weaknesses, and they aren’t necessarily difficult for attackers to exploit.
Part of the problem is how connected equipment is installed and maintained. A building control system might be installed by a specialist contractor and continue working reliably for years. Unless there’s a fault or a planned upgrade, nobody may have much reason to revisit its configuration. During that time, software can become outdated, new security vulnerabilities may emerge and updates can be missed.
Remote access arrangements can also change. An engineer who needed access during installation may no longer work for the supplier, or a maintenance contract may have changed hands. If those permissions aren’t reviewed, access that was originally legitimate could remain active indefinitely.
There can also be uncertainty over who’s responsible for security. The equipment manufacturer may look after the control software, a maintenance contractor might handle servicing, and the IT provider manages the network it connects to. Each has a role, but unless responsibilities are clearly agreed, important security checks may be missed.
For businesses, it’s worth establishing whether connected equipment is still supported, who has access to it, and whether a problem with one device could affect other systems on the network.
Six practical steps to improve your security
Its guidance highlights the importance of identifying exposed systems, controlling access and addressing known security vulnerabilities.
There are some useful steps businesses can take, even when specialist suppliers are responsible for maintaining the equipment itself.
1. Find out what’s connected to your network
Most businesses have a reasonable idea of the computers, servers and printers they use. Other connected equipment may be less obvious.
Security cameras, heating controls, building management systems and electronic access systems are all worth including in a review.
Start by identifying what’s connected and which devices can be accessed remotely. Some equipment may also use a separate internet connection, so checking your main network alone won’t necessarily give you the complete picture.
If you operate several premises, speak to the people responsible for managing each site and any contractors who maintain the equipment.
Ideally, you want a record of the systems in use, how they’re connected and who’s responsible for them. It doesn’t need to be unnecessarily complicated, but it should be accurate and kept up to date.
2. Check who has access
Remote access makes life easier for equipment suppliers and maintenance engineers. They can investigate problems and make certain changes without always needing to attend site. However, those connections need to be properly controlled.
Check whether suppliers have individual accounts or share login details. Make sure default passwords have been changed and that access is restricted to people who genuinely need it.
Multi-factor authentication should also be enabled wherever the technology supports it.
It’s worth reviewing these arrangements whenever employees leave, maintenance contracts end or suppliers change.
You may discover that everything is already managed appropriately. Or, you could find old accounts or connections that are no longer required. Either way, it’s better to know.
3. Review your network security
One of the concerns with connected equipment is what could happen if an attacker managed to compromise it.
If a device shares a network with your business computers, servers or other important systems, there may be opportunities for an attacker to move beyond the original device.
Separating certain types of equipment from the wider business network can help reduce this risk. This is known as network segmentation, and it’s one of several measures that can limit which systems are able to communicate with each other.
Firewalls and appropriate access controls also play an important role, particularly where equipment needs to be accessed remotely.
The NCSC recommends avoiding direct exposure of operational technology to the public internet wherever possible.
Any changes to specialist equipment connections should be discussed with the relevant manufacturer or maintenance provider. The network needs to be secure while still allowing the equipment to operate safely and reliably.
4. Keep ageing technology under review
Businesses naturally want to get the longest possible working life from their equipment. Replacing a functioning system can be expensive, especially when it involves specialist controls or building infrastructure.
However, older equipment can become a security concern when manufacturers stop providing updates or known vulnerabilities remain unresolved.
It’s worth checking whether your connected systems are still supported and whether recommended security updates have been applied.
For everyday IT equipment, such as firewalls, computers and network devices, regular updates should form part of normal maintenance. Specialist operational technology can be more complicated. Updates may need to be approved by the manufacturer, tested or scheduled around normal operations. If equipment can no longer be updated, work with the relevant suppliers to understand the risk and decide what additional protection or replacement planning may be necessary.
The important thing is to avoid leaving ageing systems in place indefinitely without reviewing their security.
5. Establish what’s being monitored
Security monitoring can help identify suspicious network connections, unusual remote access activity and other signs of a potential problem. However, the monitoring available for one type of equipment may be quite different from what’s possible with another. For example, your IT provider may monitor supported network equipment and business systems, while a specialist contractor looks after the operational equipment connected to them.
It’s sensible to establish what each supplier is responsible for monitoring and how potential security issues would be reported. If something unusual happened outside normal working hours, who would receive the alert? And who would be responsible for investigating it?
These arrangements are worth discussing before an incident occurs, particularly when different suppliers manage different parts of your technology.
6. Make sure you have a plan for disruption
The recent supermarket incidents illustrate how a cyber attack involving connected equipment can have consequences for normal business operations. It’s worth considering how your own organisation would cope if an important system stopped working unexpectedly.
The appropriate response will depend on the sector you are in and the equipment involved, but staff should know who to contact and what action they’re authorised to take.
Where specialist systems are concerned, recovery procedures should be agreed with the people who understand how that equipment operates. This may include maintaining configuration backups, documenting emergency contacts and establishing safe procedures for isolating affected systems.
A business continuity plan should reflect these arrangements and be reviewed when equipment, suppliers or operational requirements change.
Where does your IT provider fit in?
One of the challenges with connected equipment is that responsibility is often shared between several suppliers.
An HVAC contractor may maintain the heating and ventilation system, for example, while the manufacturer provides software updates and your IT provider manages the business network.
That’s a perfectly normal arrangement. Problems can arise, however, if nobody has established who’s responsible for securing the connections between those systems.
Specialist equipment suppliers are generally best placed to advise on their own control systems and maintenance requirements. Your IT provider can help with the security of the network, remote access arrangements and the supported IT infrastructure that equipment connects to.
At PS Tech, we work with businesses across Sussex and the South East. Our services include network and infrastructure support, cyber security services and managed IT support.
We help businesses review their IT security arrangements, identify vulnerabilities within the scope of an assessment and make improvements to their supported networks and infrastructure.
Where specialist equipment is involved, its manufacturer or maintenance provider will need to advise on the security and operation of the equipment itself.
Having clear responsibilities between suppliers makes it easier to address potential weaknesses and ensure important connections aren’t overlooked.
How secure is your business’s connected technology?
The recent refrigeration attacks are a reminder that a cyber security incident can cause disruption well beyond the usual IT systems.
Most businesses now rely on connected equipment in one form or another, whether that’s building access, security cameras, heating controls or specialist machinery.
It’s worth taking the time to understand how those systems connect to your network, who has access and whether the appropriate security measures are in place. Some of the checks may be straightforward. Others will need input from your IT provider, equipment manufacturers or maintenance contractors.
If you’re unsure about the security of your business network or the systems connected to it, PS Tech can help you review your IT arrangements, identify potential weaknesses and understand where improvements may be needed.
Get in touch with PS Tech to discuss your business’s IT infrastructure and cyber security.
Frequently Asked Questions About Connected Equipment and Cyber Security
Can hackers really access equipment such as freezers and heating systems?
Yes. Some refrigeration, heating and building management systems can be monitored or controlled remotely. If those connections aren’t properly secured, attackers may be able to gain unauthorised access. The recent supermarket refrigeration incidents are an example of how a cyber attack involving connected equipment can affect physical business operations.
What types of connected equipment could pose a cyber security risk?
Any network-connected device could potentially introduce a security risk if it isn’t properly configured or maintained. This includes security cameras, electronic door controls, heating and ventilation systems, building management equipment and specialist machinery. The level of risk depends on how the equipment connects to other systems, who can access it and what could happen if it was compromised.
How can I tell if my business has insecure connected devices?
Start by identifying the equipment connected to your network and checking which systems can be accessed remotely. Look for default passwords, outdated software, unnecessary remote access and equipment that no longer receives security updates. Your IT provider can help assess the supported network infrastructure, while specialist equipment suppliers may need to check the devices and control systems they maintain.
Should connected equipment be kept separate from our main business network?
In many cases, separating connected equipment from computers, servers and other business systems is a sensible security measure. Known as network segmentation, this can help restrict access between systems and reduce the potential impact of a compromised device. The appropriate arrangement will depend on the equipment involved and its operational requirements.
Who is responsible for securing connected equipment?
Responsibility is often shared. Equipment manufacturers and maintenance contractors may manage specialist control software, updates and servicing, while an IT provider looks after the network and supporting infrastructure. Businesses should establish who is responsible for each part of the system, including remote access, security updates, monitoring and incident response.
Can an IT support provider help protect connected business equipment?
An IT support provider can help secure the network and IT infrastructure that connected equipment uses. This may include reviewing network configurations, improving access controls, assessing vulnerabilities within an agreed scope and strengthening network security. Specialist operational equipment may need separate assessment and maintenance by its manufacturer or an appropriately qualified contractor.